Risk Management
To avoid losing enterprise value and the trust of the public, the azbil Group strives to accurately understand and minimize risk factors with the potential for serious impact on operations.
The azbil Group's Risk Management
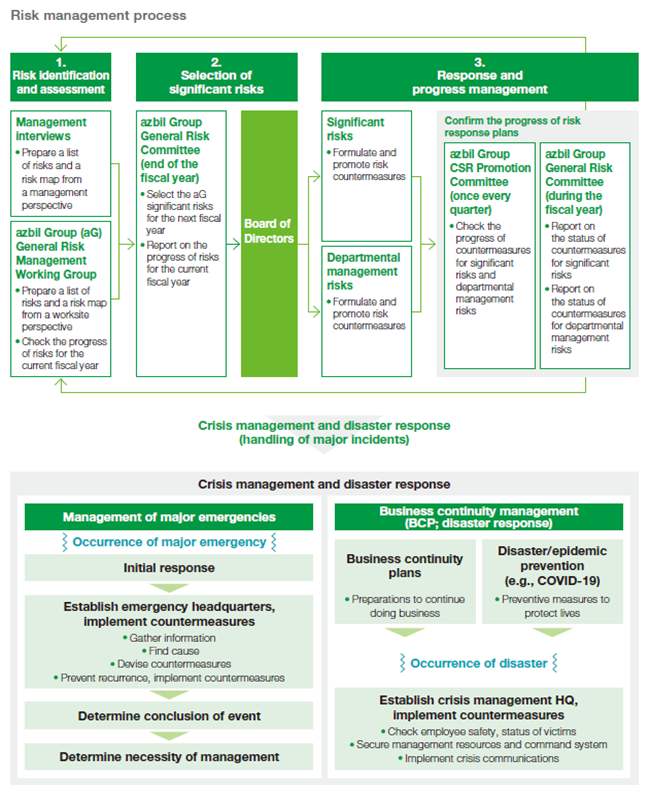
To minimize risk from possible future events, we comprehensively identify risks every year, taking changes in the internal and external environment into account. Then we select significant risks based on quantitative standards such as the financial impact and likelihood of those risks. To realize meticulous risk management that integrates bottom-up and topdown approaches, we have adopted a procedure to ensure that top management has a full understanding of the information from the bottom (departments handling on-site work), enabling more informed decision-making. Of the 122 risks comprehensively identified in FY2026, we selected 18 as risks deemed important to the azbil Group (the significant risks) that would have a severe impact on the business of the Group, and categorized other risks as epartmental management risks. Significant risks are handled by officers who are fully responsible for those risks, whereas departmental management risks are handled by the head of the corresponding department. They both formulate and promote plans for reducing risks. Quarterly reports on the progress of implemented measures are provided to the general risk management department and executive officer in charge of risk management, who is ultimately responsible for the risk management of the Group. These reports are made at the azbil Group CSR Promotion Committee meetings, which are attended by department managers and officers in charge of CSR at Group companies. Significant risks are further discussed at semiannual azbil Group General Risk Committee meetings, which are attended by the members of Azbil’s Management Meeting and headed by the executive officer in charge of risk management. At these meetings, the progress and effectiveness of risk mitigation plans are confirmed, the impact and/or likelihood of these risks occurring at the end of the fiscal year are managed to ensure risk reduction, and these efforts are improved through the PDCA cycle.
As part of crisis management and disaster response, we have also established a crisis management response system to minimize the impact of incidents. For each incident, an emergency headquarters led by the responsible officer is established to investigate the cause, implement countermeasures, and prevent recurrence. The status of such efforts is reported quarterly at Azbil’s Management Meetings and Board of Directors meetings. Furthermore, we have formulated many kinds of detailed business continuity plans (BCPs) as we continuously strive to improve our systems as part of our business continuity management.
Risk Management System
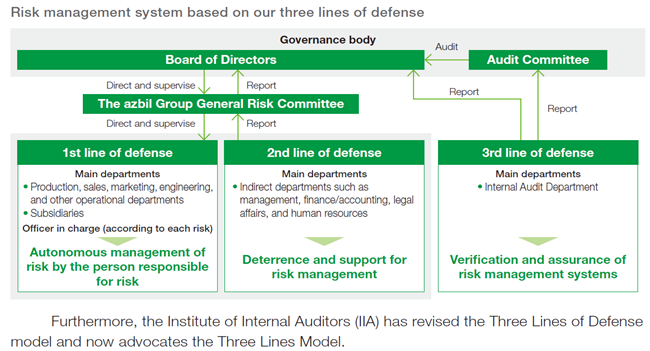
The azbil Group manages risk based on three lines of defense. In the Group’s overall activities, we are working to improve the organization’s internal control and risk response functions through three lines of defense, with clearly defined responsibilities. As the first line of defense, we are strengthening autonomous management by clearly identifying an officer responsible for each risk. As the second line of defense, indirect departments are primarily responsible for developing and managing countermeasures and providing support for risks that should be addressed by the entire organization, thereby functioning to deter risk and support risk management. As the third line of defense, the Internal Audit Department verifies and ensures the risk management systems of the first and second lines of defense. The azbil Group conducts a comprehensive identification of risks that could have a significant impact on management and assesses their degree of impact and likelihood of occurrence. Through interviews with management, risks are identified and evaluated from a management perspective. In addition, the azbil Group General Risk Management Working Group, comprising department heads, identifies and evaluates risks from a worksite perspective and consolidates the results of these two activities into an integrated risk register, which summarizes risk details and evaluations, and a risk map that plots risks on a 5×5 matrix based on impact and likelihood of occurrence. The azbil Group General Risk Committee deliberates on this data and selects significant risks, which are then reported to the Board of Directors.
Business-Related and Other Risks
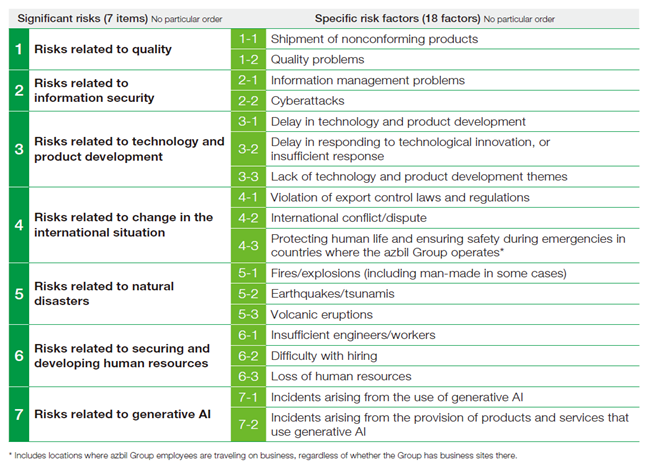
Significant risks that could severely affect the business results and financial position of the azbil Group are summarized below. Of the 122 risks comprehensively identified, we selected 18 as significant risks, and summarized these into seven items. The significant risks indicated below and the specific risk factors are judged by Azbil to be valid as of the end of FY2025. Details on risk awareness and countermeasures for each significant risk are found in the 104th Securities Report.
Improving Disaster Prevention Capabilities and Business Continuity Plan (BCP)
The azbil Group takes various disaster prevention measures to minimize potential damage to its operations and improve its disaster response capabilities. For example, we regularly verify the earthquake resistance levels of our buildings and work to strengthen them. We also conduct hazard inspections, stockpile inspections, and disaster prevention drills, and we are developing an emergency communication infrastructure. In addition, we are promoting the use of DX to forecast and visualize disaster information and strengthen our employee safety confirmation system.
Through our BCP, we aim to fulfill our responsibility to society by ensuring that the survival of the entire azbil Group is not threatened, while also preventing serious suspensions and delays in operations, with a top priority of guaranteeing the safety of human life. Our basic policy is to normalize corporate activities without causing delays to the restoration of society. We have created various disaster scenarios, based on which we analyze the current situation and formulate countermeasures for each business, production, and administrative function while conducting relevant training. We have also secured offices, restored important systems and networks, and performed financial simulations. We remain committed to prioritizing the safety and security of our customers and employees, and will continue enhancing our disaster response capabilities and strengthening our business continuity planning (BCP).
Reinforcing Our Information Management System
We are using IT systems in various ways, such as strengthening network and authentication infrastructures to enable employees to work safely from external locations. Our aim is to maintain high levels of safety and security even for employees working from home. In addition, to prepare for cyberattacks such as ransomware, we continue to operate our incident response framework and conduct practical training. In addition, we conduct information security training annually for all Group employees. We also address information management issues identified via our compliance awareness survey, and we have a system to ensure proper compliance with laws and regulations on the protection of important information, including personal information, in each country/region. In these and other ways, we are working to improve and strengthen our Group-wide information management system.